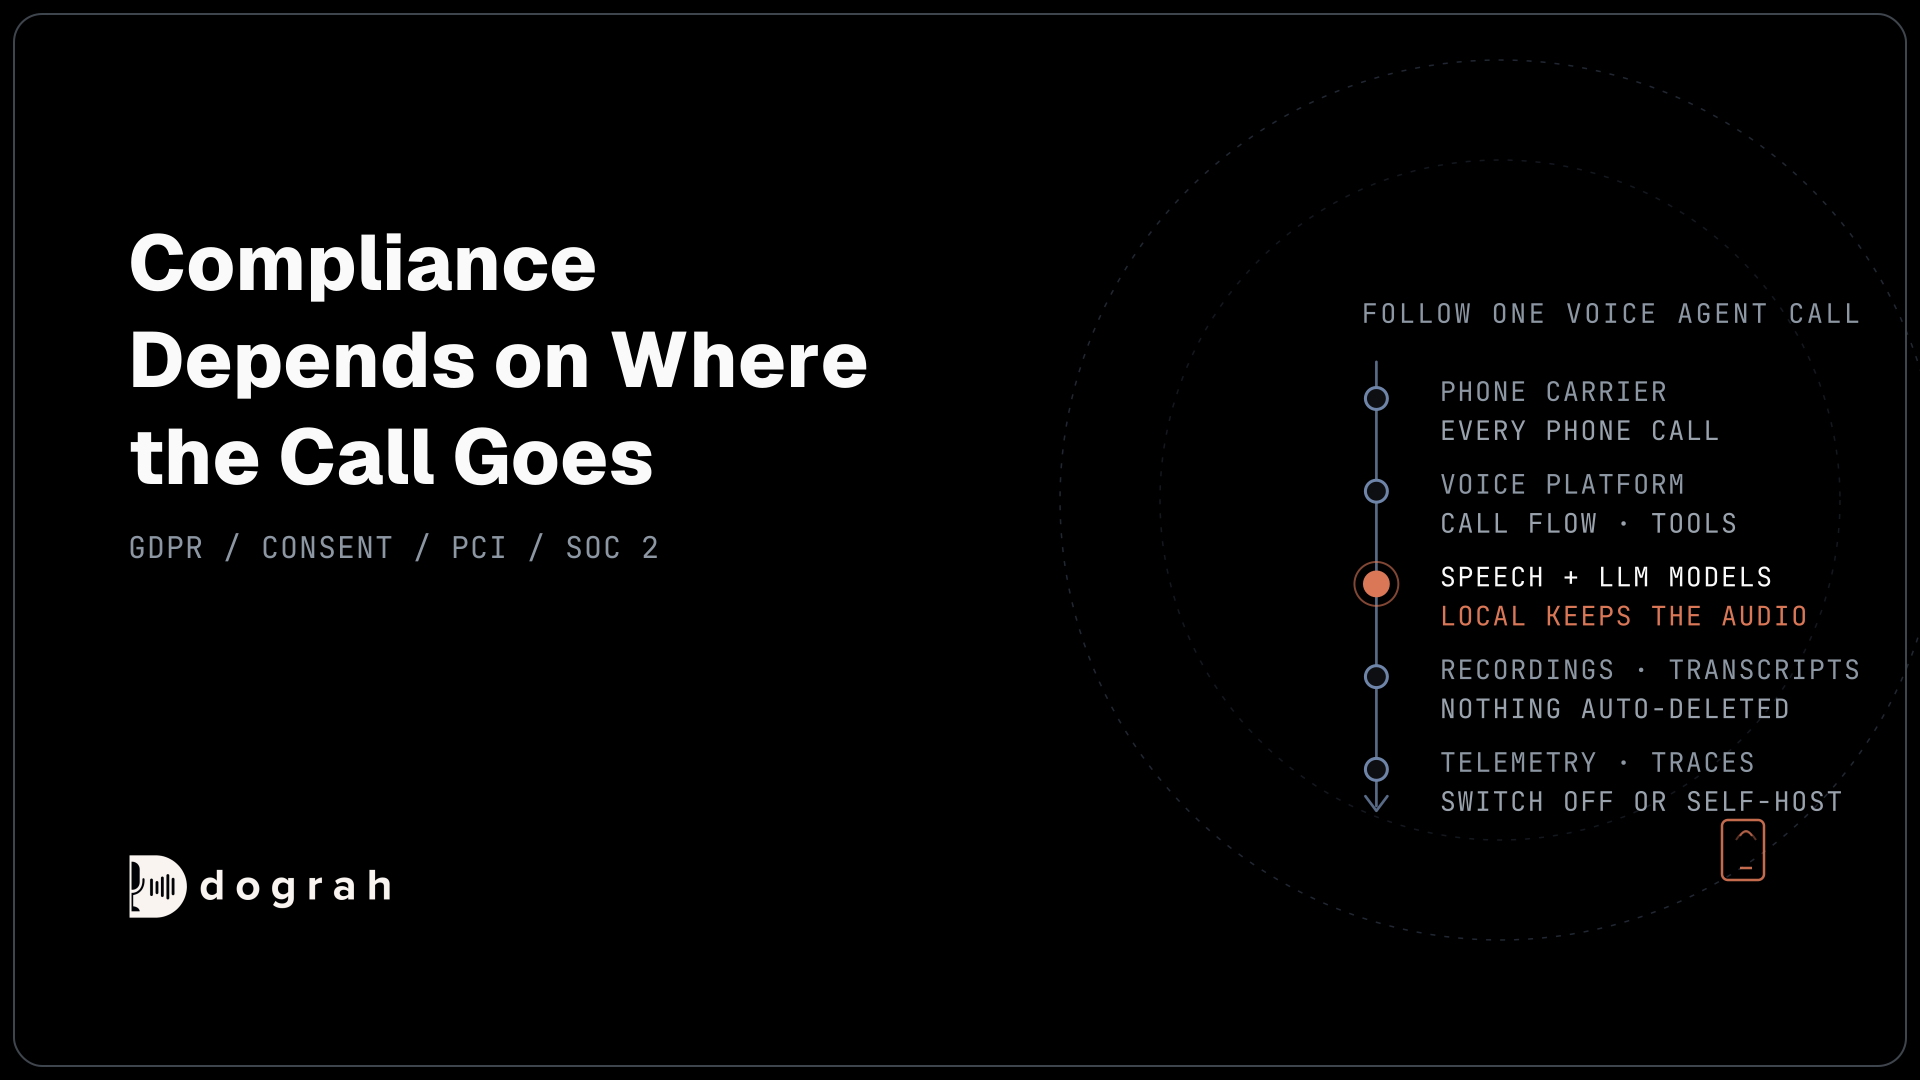
The Complete Guide to Compliant AI Voice Agents: Follow the Data
A guide to compliant AI voice agents: every place a call's data goes, what self-hosting keeps on your servers and what still leaves, and how GDPR, recording consent, payment calls, SOC 2 reviews and procurement apply.
Read the full guide →Deep Dives in This Series
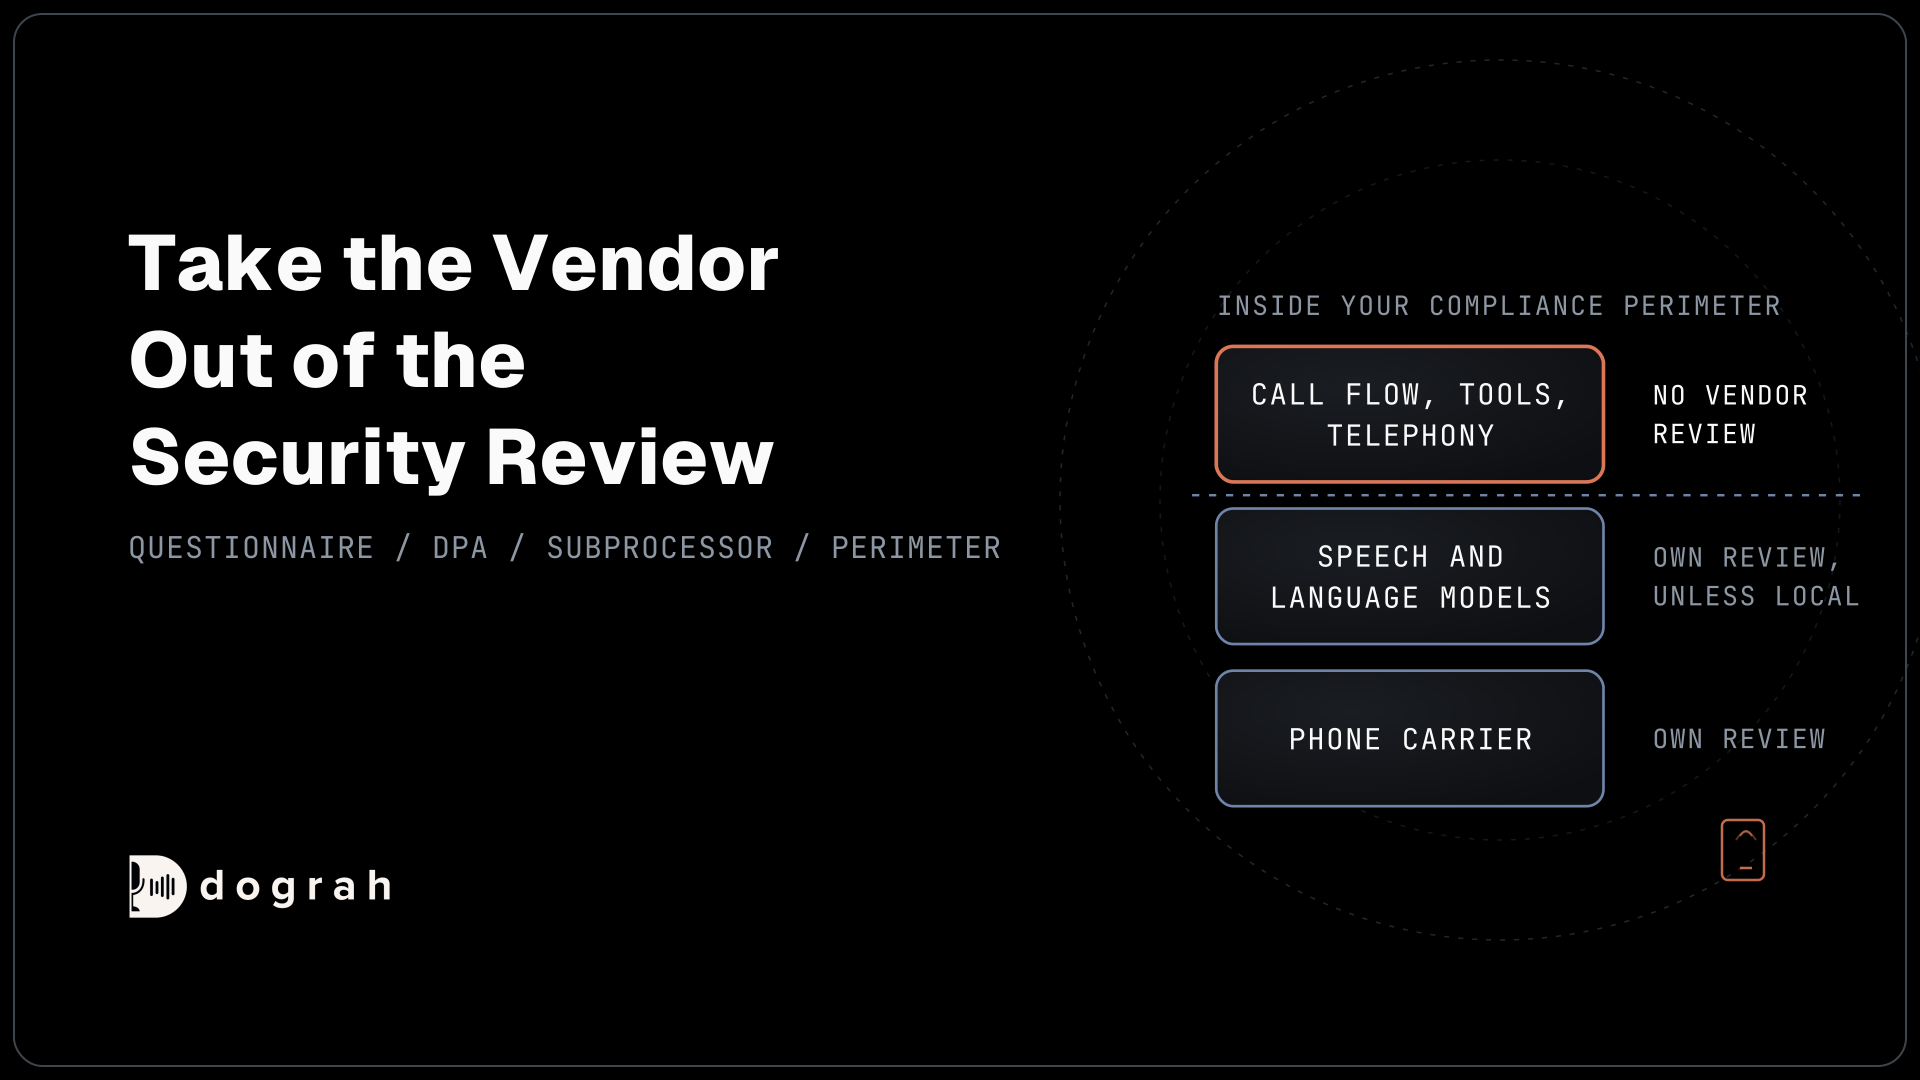
Why Procurement Stalls on Closed Voice Vendors (and How to Skip It)
Why buying a closed voice AI vendor stalls at the security review, which questionnaire rows fall away when you self-host an open-source platform inside your compliance perimeter, and what your team and your model providers still have to review.
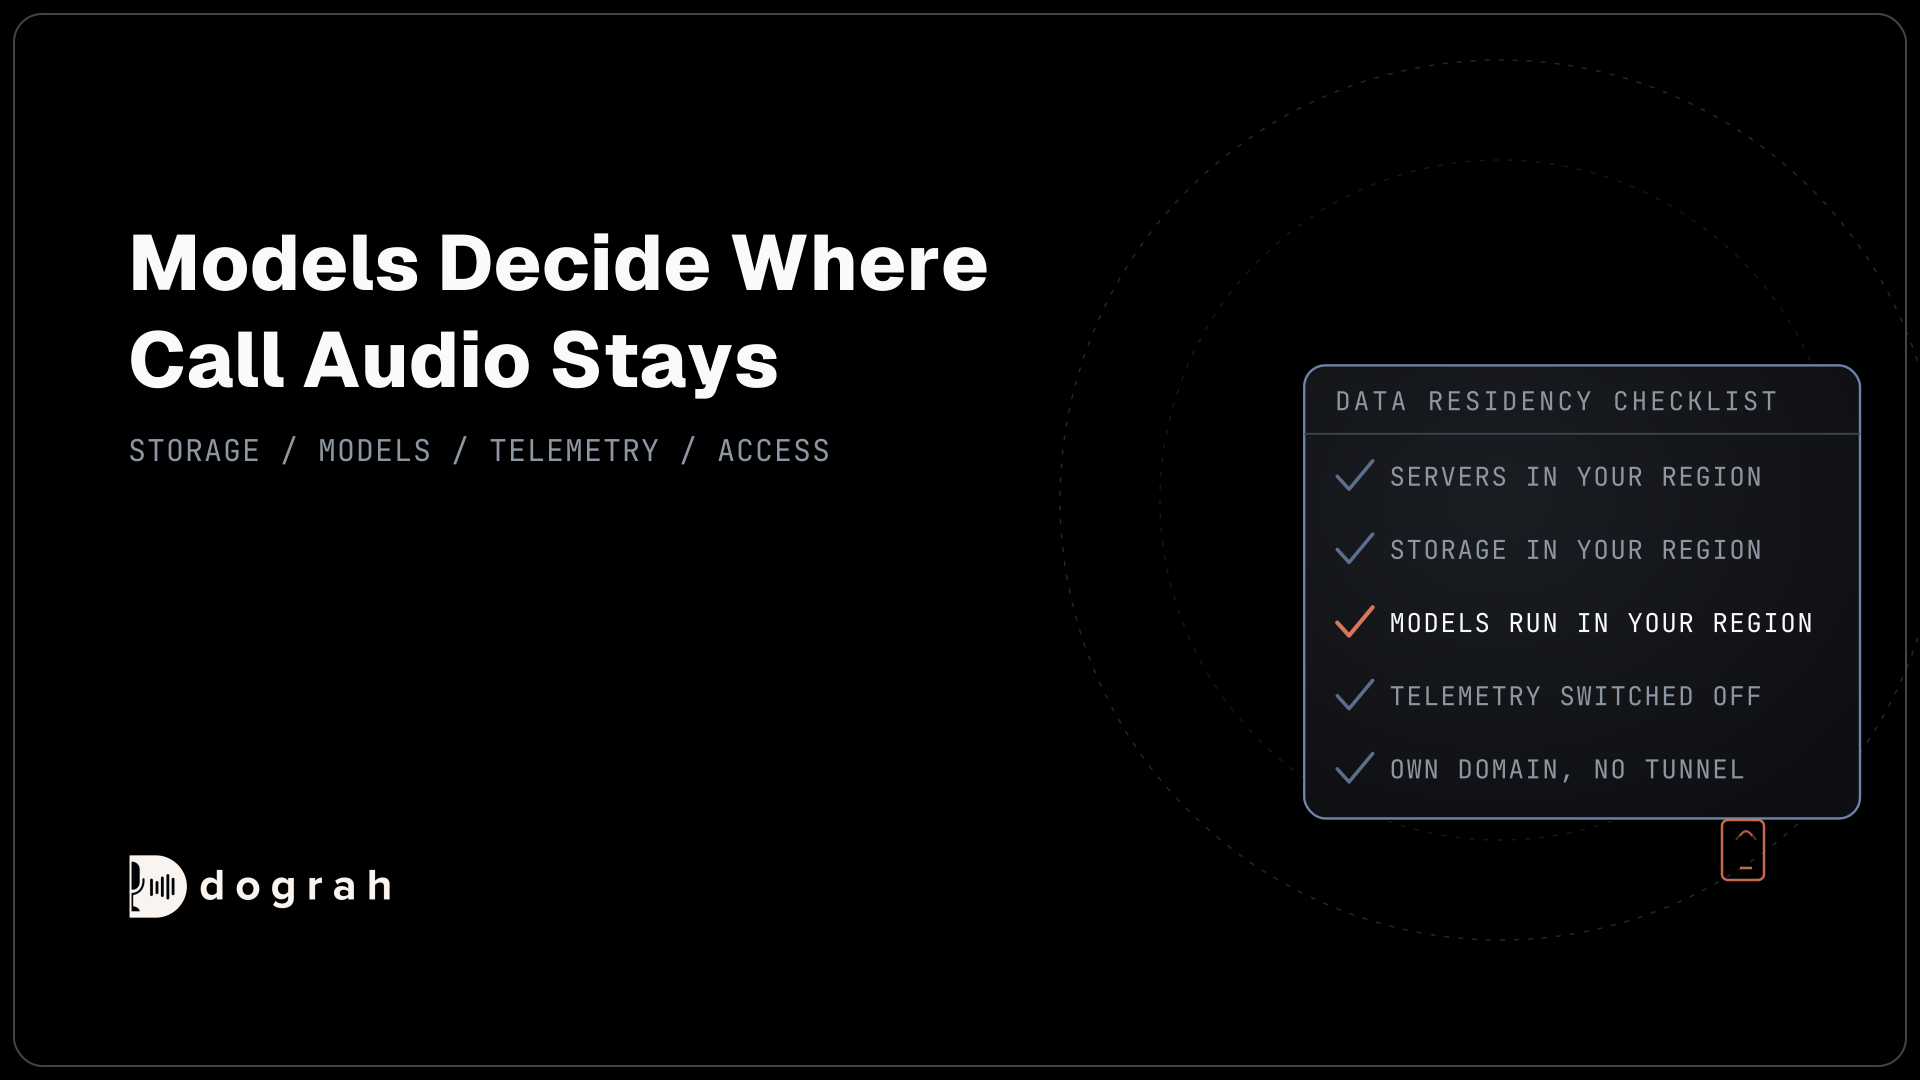
Data Residency for Voice AI: A Buyer's Checklist of Every Setting
A buyer's checklist for data residency in voice AI: every place a call's data goes, from servers and models to the phone carrier, telemetry, the quickstart tunnel, tracing, tools and remote access, with the setting that keeps each one in your region.
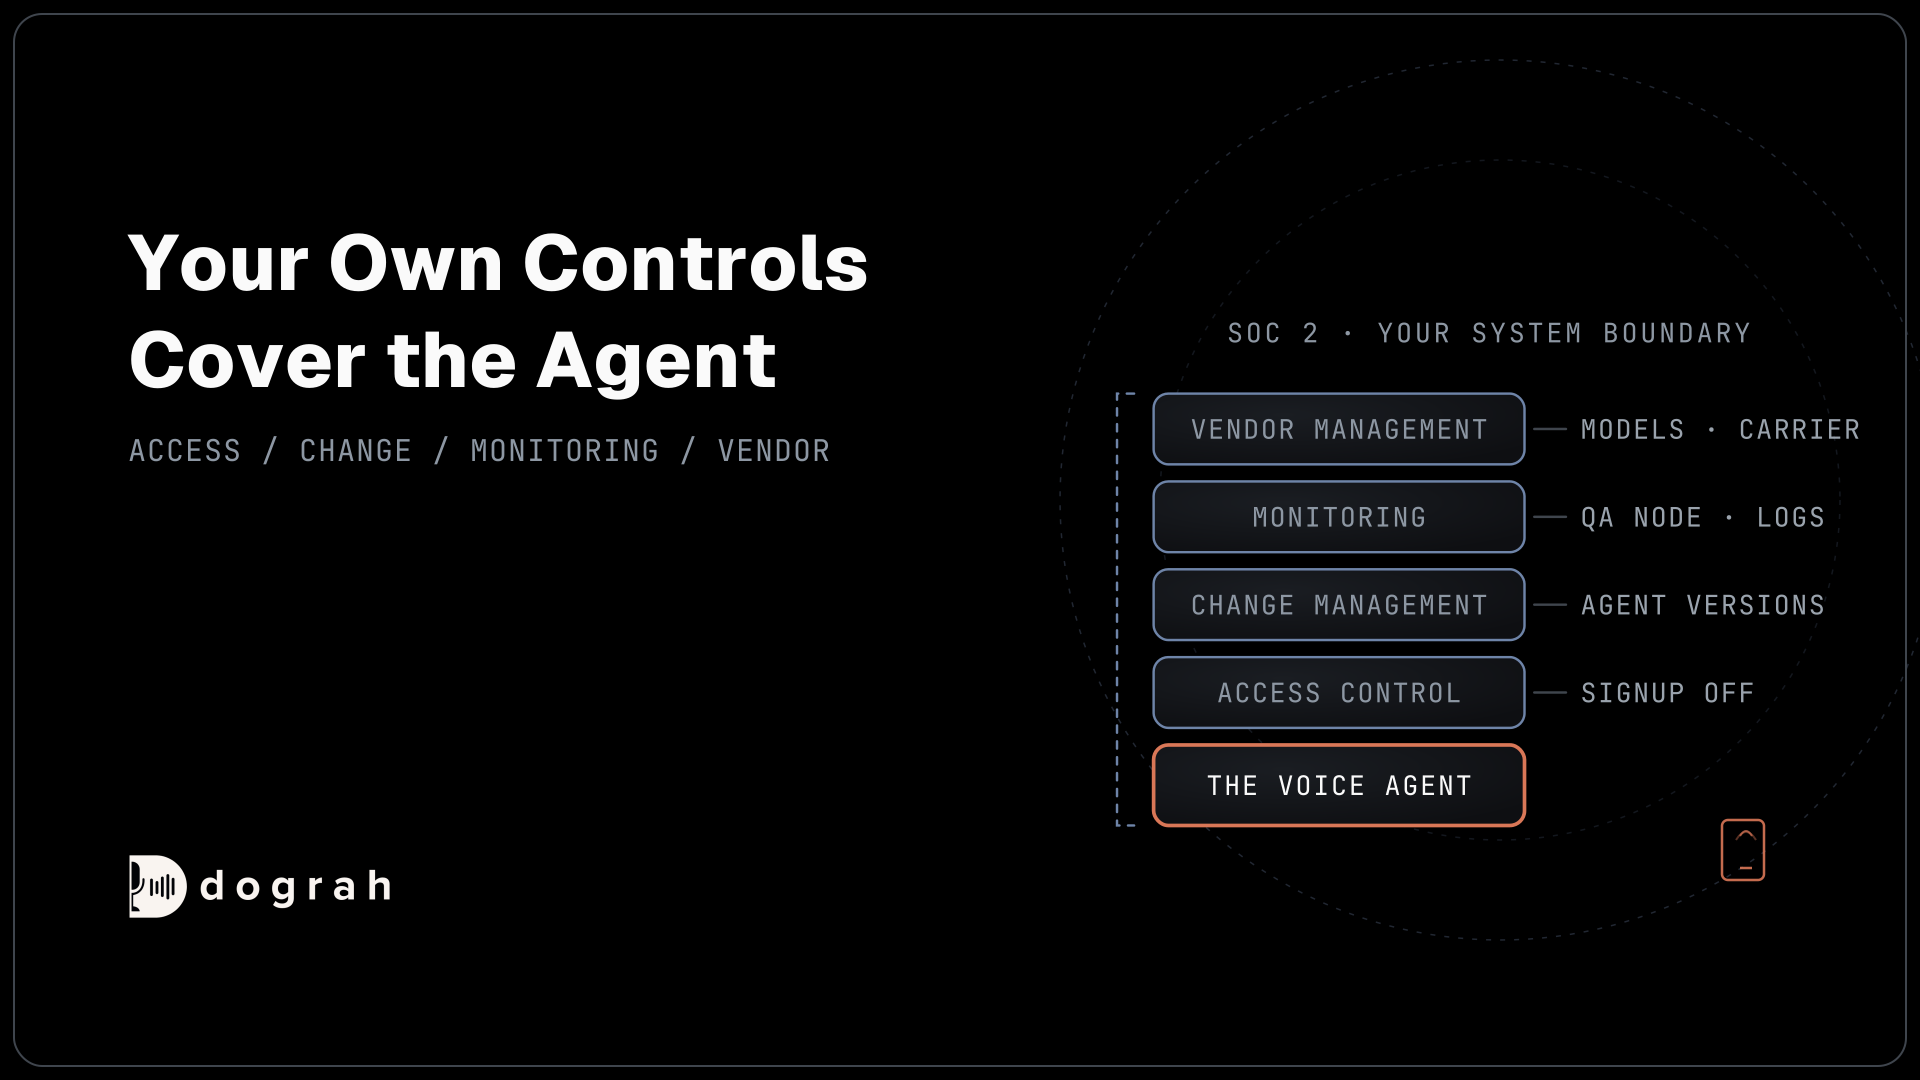
How to Pass a SOC 2 Review With a Self-Hosted Voice Agent
How a self-hosted voice agent fits a SOC 2 review: why it sits inside your own system boundary, where its call data lives, the defaults to close before an audit, the change evidence it keeps, and which outside vendors still need review.
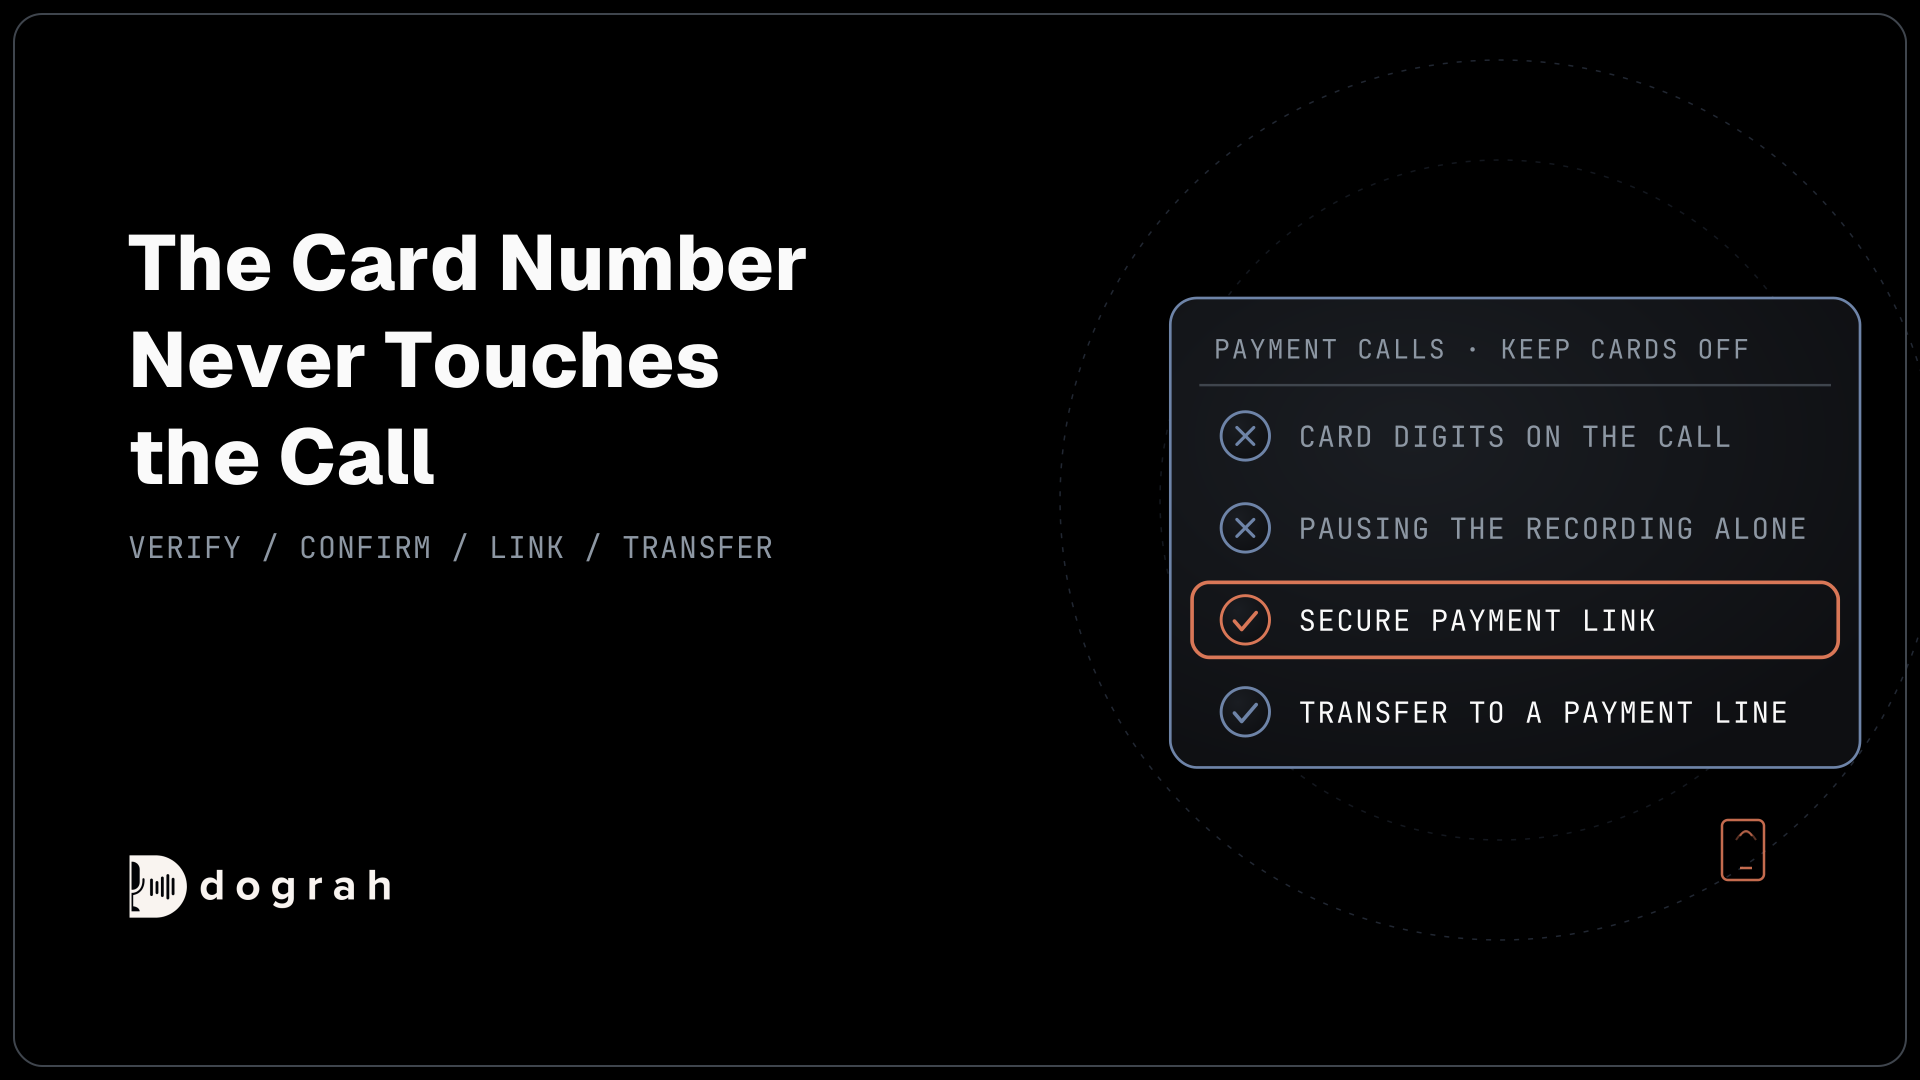
Handling Payment-Sensitive (PCI) Calls in a Voice Agent Safely
How to handle payment-sensitive calls in an AI voice agent: where a spoken card number ends up, what PCI DSS says about card data in recordings, why pausing the recording falls short, and two designs that keep card data off the call.
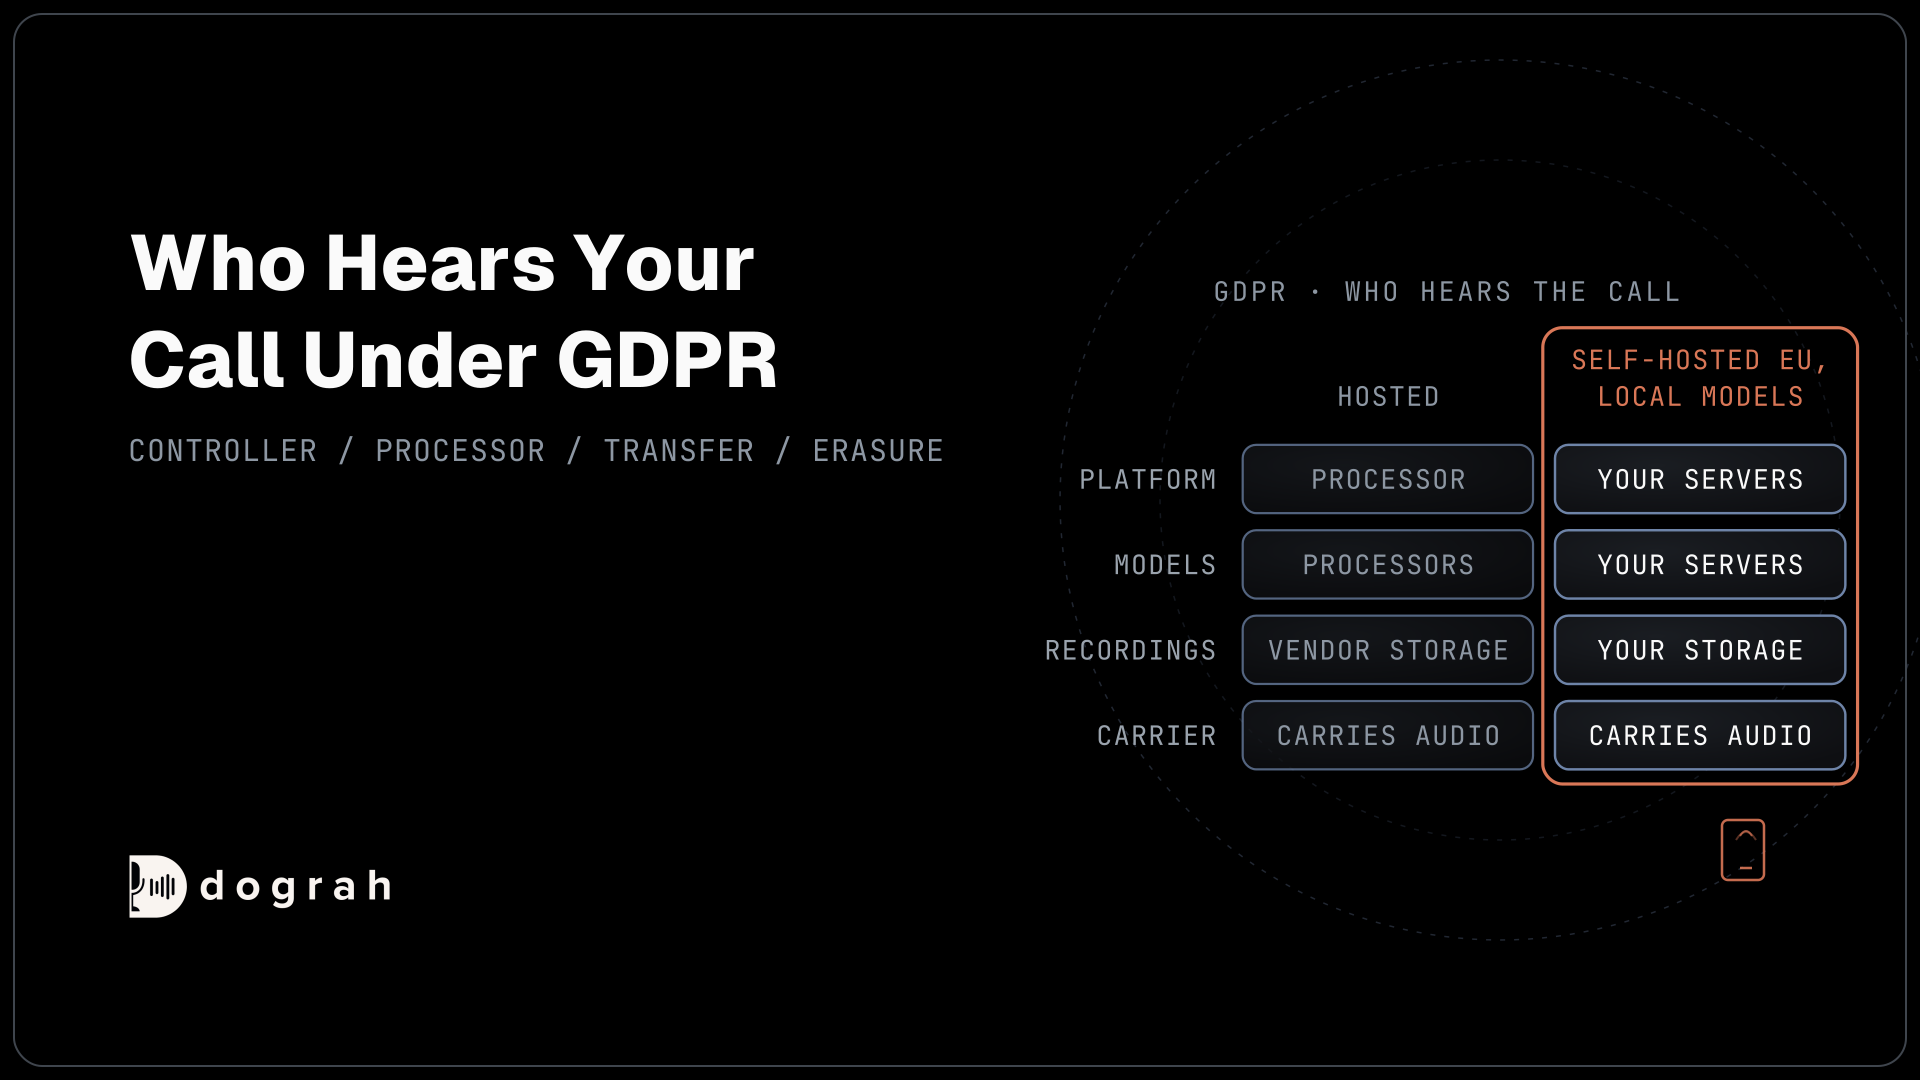
GDPR and Voice AI: Keeping Call Data Inside Your Borders
How the GDPR applies to AI voice agents: voice as personal data, the controller and every processor that hears the call, transfers and remote access, what self-hosting in the EU with open-weight models keeps in-region, and AI disclosure under the AI Act.
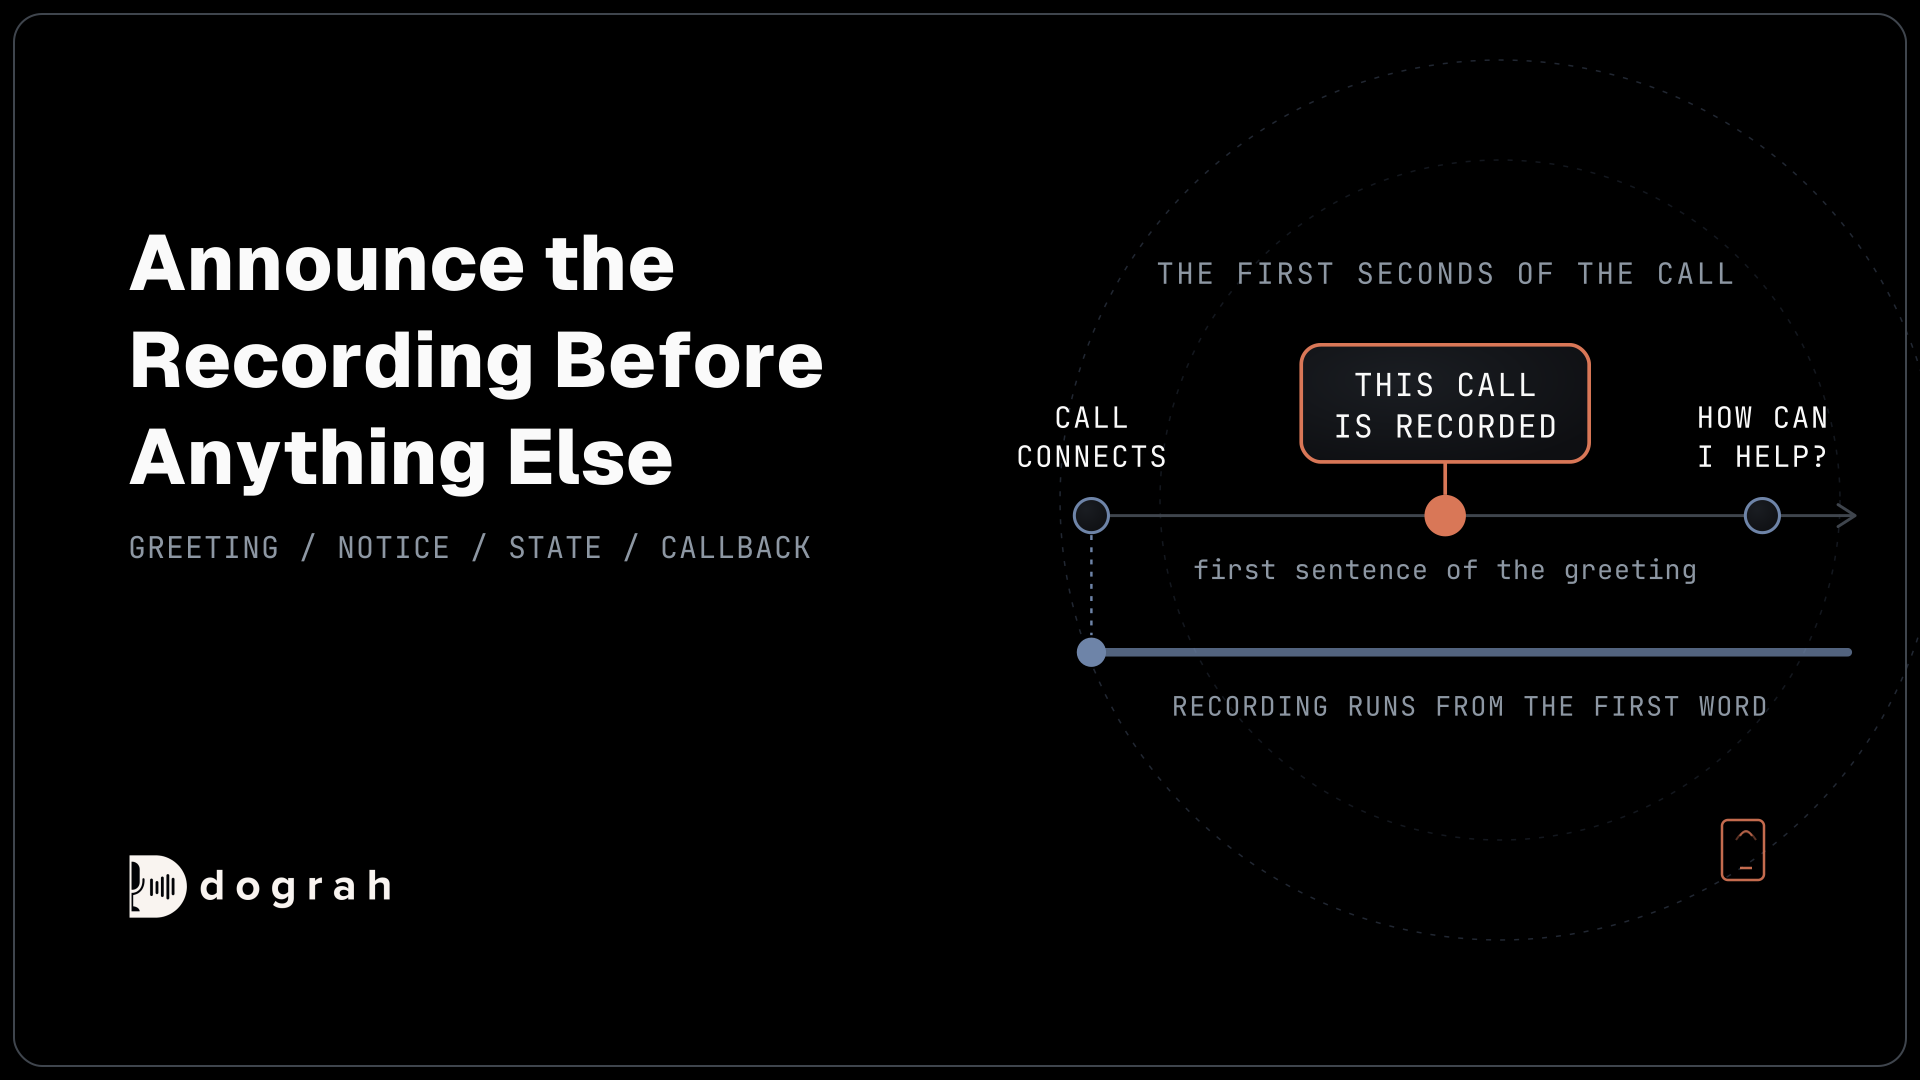
Call-Recording Consent Laws and How to Configure Your Agent
Call-recording consent laws quoted from the statutes (federal, California, Florida, Illinois and Washington), and how to configure a voice agent: a fixed recording notice at the start of the greeting, what to do when a caller talks over it or says no, and interstate calls.
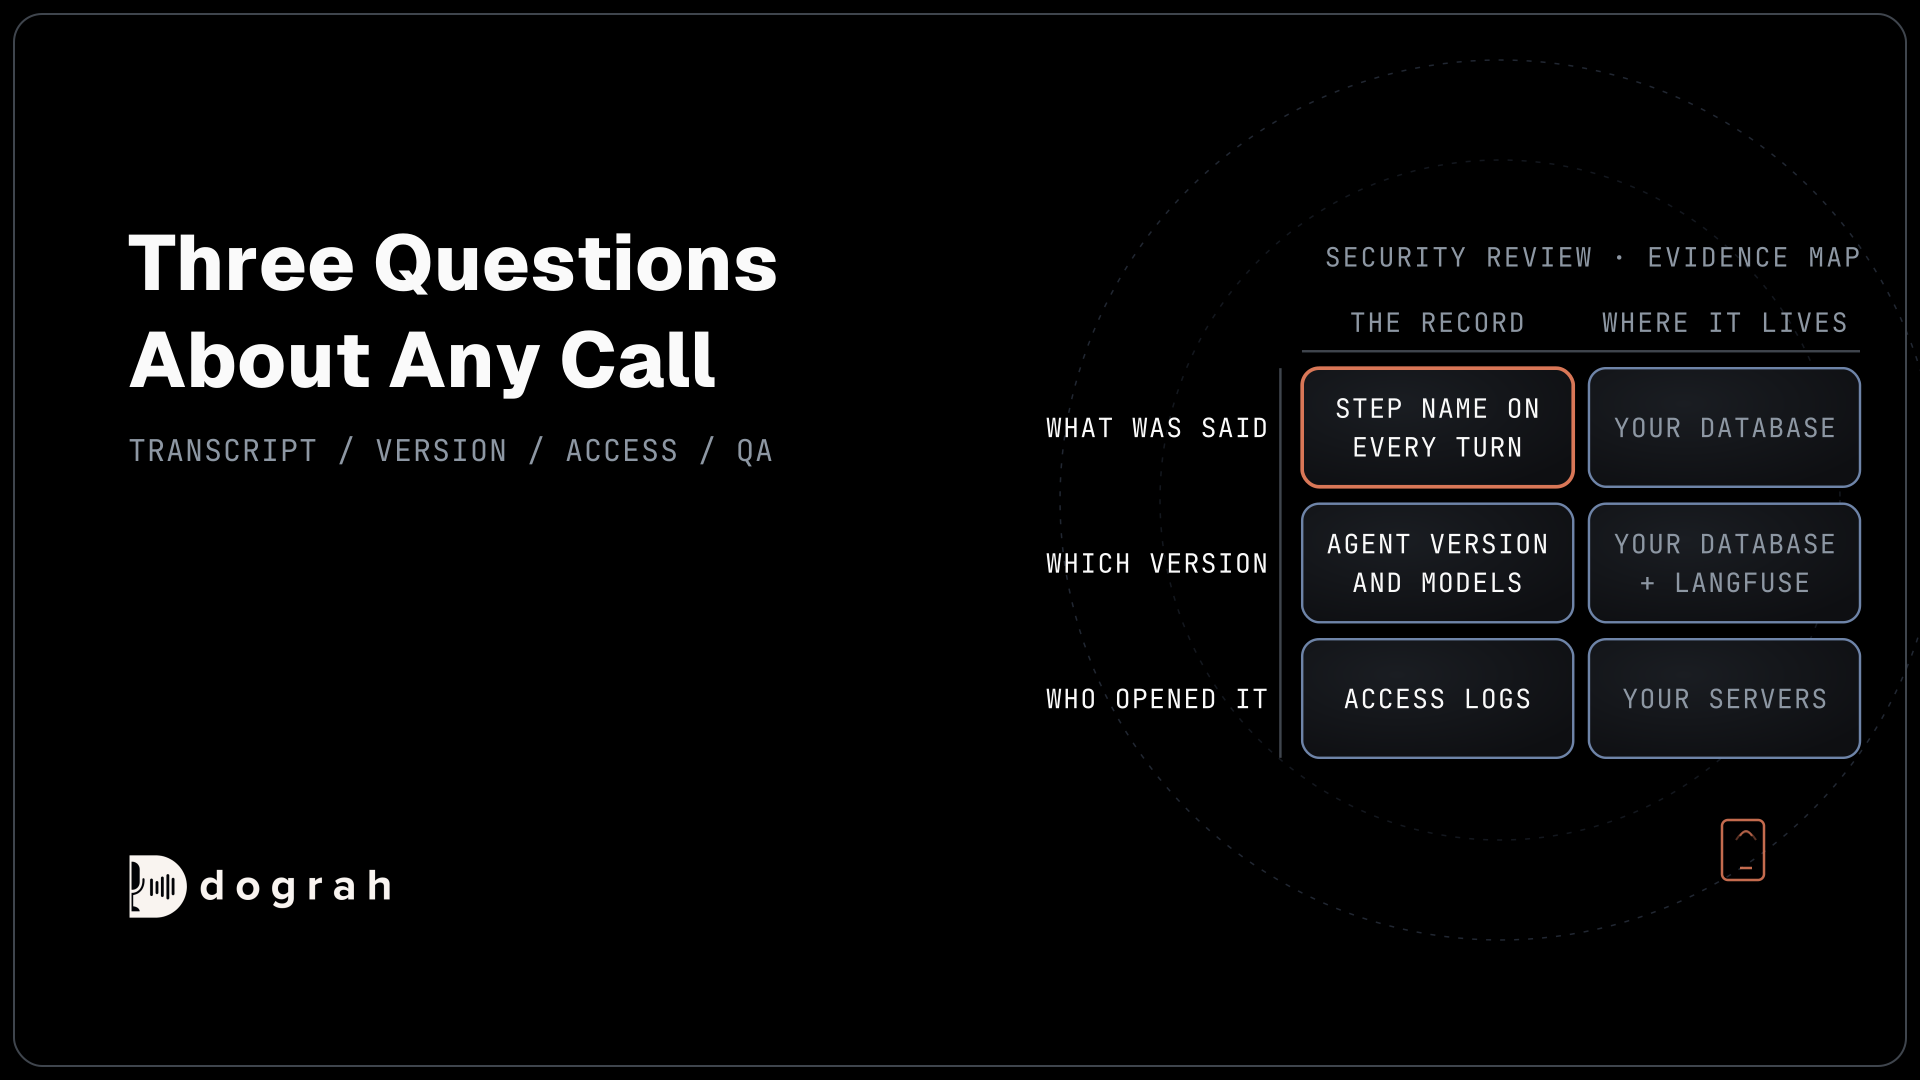
Building an Auditable Voice AI Stack for Security Reviews
How to build a voice AI stack a security reviewer can audit: step-tagged transcripts, tool calls, the agent version and model settings behind every call, access logs for who opened the records, and QA sampling, mapped to NIST SP 800-53.